Discover
Use inventory and device groups to identify operating systems, existing versions, available endpoints, and customer boundaries.
Use DeskGate device groups and remote administration workflows to distribute approved Windows software without visiting every office, home, branch, or customer location.
Remote software deployment is the controlled delivery and installation of an application on one or more computers from a central administration environment.
It reduces the need for a technician to connect interactively to every endpoint. A deployment workflow typically includes identifying eligible devices, preparing the installer and required parameters, selecting a controlled target group, scheduling or initiating execution, reviewing results, and following up on exceptions.
DeskGate connects remote software deployment with company, group, endpoint, inventory, command, script, and support context. This is useful for internal IT teams with many offices and for service providers managing customer devices. Central delivery improves consistency, but it must be supported by package testing, authorization, maintenance windows, logging, and recovery planning.
Use inventory and device groups to identify operating systems, existing versions, available endpoints, and customer boundaries.
Prepare the approved installer, silent parameters, prerequisites, validation method, and rollback procedure.
Deploy to representative devices and verify application behavior, endpoint stability, logs, and business workflow.
Roll out in manageable groups with maintenance windows, named owners, and exception handling.
Document targeted devices, results, failures, retries, support demand, version status, and final acceptance.
An installer that works manually may fail under a service account, outside an interactive desktop, or when a prerequisite is missing. Confirm architecture, supported Windows versions, disk space, required services, reboot behavior, dependencies, licensing, certificate trust, proxy requirements, and security software interaction.
Use vendor-supported silent installation parameters and avoid embedding reusable credentials in packages or scripts. Determine how success will be verified: installed version, service state, registry value, executable presence, application inventory, or another reliable signal. Define how partial installation will be cleaned up and when a technician must intervene.
Packages should have clear ownership and versioning. Record the source, checksum where appropriate, approval, creation date, supported target, parameters, pilot outcome, and retirement date. Replace obsolete packages so technicians do not accidentally distribute an unsupported build.
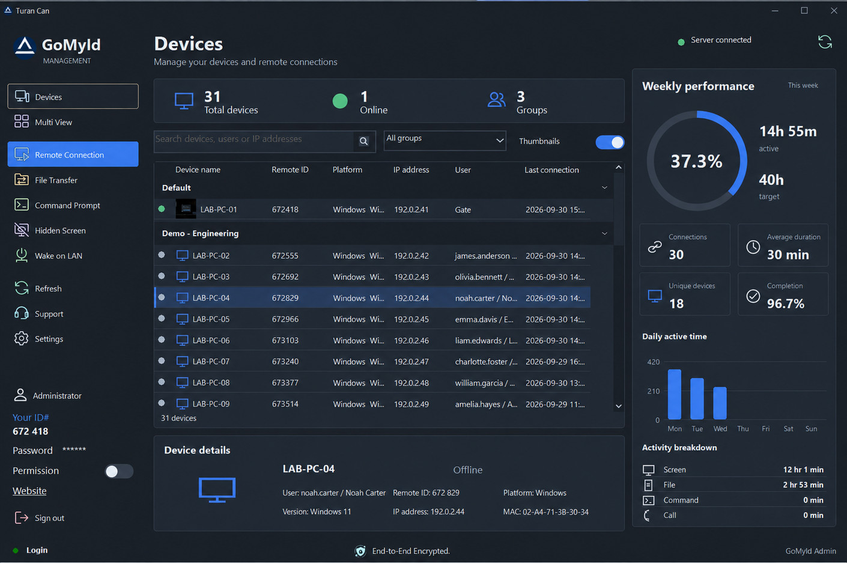
Device grouping makes deployment scalable, but a broad group can also amplify a mistake. Select targets by company, department, customer, operating system, device role, location, or rollout wave. Exclude critical systems and unavailable users when their operational conditions require a separate plan. Confirm that an MSP package cannot cross customer boundaries.
Schedule disruptive installations during an approved maintenance window and communicate expected behavior. Tell users whether applications will close, a reboot may occur, or a temporary performance impact is expected. Maintain an escalation contact for business-critical problems. A phased rollout provides time to stop expansion when pilot assumptions do not hold.
Only authorized administrators should create, approve, target, and execute software packages. Separate package preparation from broad production approval where organizational risk requires it. Protect the central package repository, installer sources, signing certificates, database, administration accounts, and endpoint communication.
Review logs for unexpected targets, repeated failures, modified parameters, or installation outside approved periods. Remote deployment can improve endpoint security by distributing patches and approved tools, but unauthorized deployment can create an equally serious risk. Treat deployment rights as privileged access and remove them promptly when roles change.
Verify online state, service health, network path, firewall policy, and whether the device is inside the intended company and group. Retry according to a controlled schedule rather than creating unlimited repeated attempts.
Detect required runtime, framework, service, free space, or prior version before installation. Use a preflight script only after testing it on representative systems.
Validate installer reputation, signing, approved exclusions, and policy through the organization’s security process. Do not disable endpoint protection broadly to force installation.
Define reboot behavior, user notification, deferral rules, and the recovery path. Avoid interrupting active work without an approved urgent security reason.
After deployment, compare target inventory with the expected version and review failures by cause. Close the change only after technical validation and business acceptance. Retain evidence appropriate to the organization’s change-management and customer-reporting requirements.
Show us your endpoint groups, applications, installation rules, customer boundaries, and reporting expectations for a focused DeskGate demonstration.
Completion should mean more than receiving a successful process exit code. Confirm that the expected application version appears, required services start, shortcuts and integrations behave correctly, users can perform the approved workflow, and security controls remain active. Compare the final state with a documented acceptance condition.
Plan for the next version before closing the rollout. Record which devices were excluded, which require manual remediation, and which package must be retired. Application ownership should include update cadence, vulnerability response, licensing, uninstall behavior, and end-of-support dates.
For customer environments, keep package approval and reporting within the correct company boundary. Provide a concise service record showing scope, schedule, result, exceptions, and follow-up without exposing unrelated device or user information. This makes remote deployment a repeatable change-management capability instead of an undocumented administrative shortcut.
Include application owners and affected business teams in final acceptance so technical installation and practical usability are verified together.