Data location
Select the server, SQL database, backup location, network route, administrator boundary, and recovery process used for operational records.
DeskGate provides on-premise Remote Desktop capabilities for organizations that want secure endpoint access without making a vendor-controlled cloud the center of their support architecture.
Self-hosted Remote Desktop software runs the central administration and supporting data components in infrastructure selected and operated by the customer or its authorized service provider.
The organization decides where the server and database reside, which network boundaries apply, who administers the platform, how backups and recovery work, and how long operational records are retained. Endpoints still require secure communication and appropriate permissions, but the deployment does not depend on placing the core management data in a vendor-controlled multi-tenant cloud.
DeskGate combines Remote Desktop with device organization, file transfer, commands, support workflows, reporting, and Management RMM capabilities. This makes self-hosting relevant not only to an individual connection, but also to the full operational process around endpoint support.
Select the server, SQL database, backup location, network route, administrator boundary, and recovery process used for operational records.
Align authentication, firewall policy, monitoring, incident response, patching, certificates, and privileged administration with internal standards.
Organize companies and groups for internal departments, branches, dealers, or managed customers while maintaining explicit access scope.
Plan capacity, backups, restoration, maintenance, and upgrades around business requirements rather than an external service status alone.
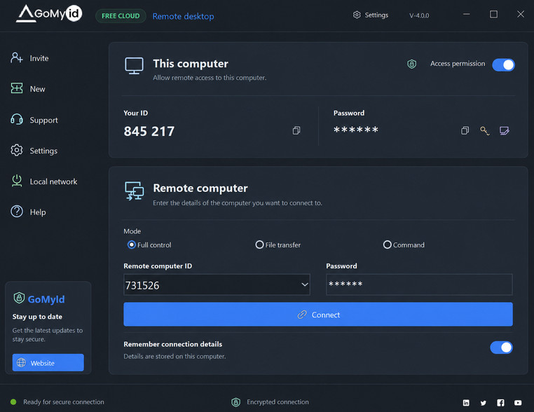
An on-premise deployment gives the organization more decisions and more responsibility. The server, database, network, backups, administrative accounts, endpoint service, and update process must be secured and maintained. Poorly configured self-hosting can be less secure than a well-operated hosted service.
Assign named platform, security, database, network, support, and governance owners. Use least privilege, supported encryption, firewall restrictions, strong authentication, patching, logging, backup testing, and incident response. Review Remote Desktop permissions and customer boundaries on a schedule.
Estimate endpoint count, concurrent connections, companies, administrators, reports, database growth, retention, screen characteristics, and support activity. Select supported Windows Server and SQL Server resources with headroom for growth. Separate production responsibilities and document dependencies before pilot installation.
Prepare network routes, firewall rules, certificates, DNS where applicable, service accounts, backup targets, monitoring, and recovery. Test endpoint communication from representative offices, homes, branches, and customer networks. Validate behavior when a route is interrupted and when services restart.
Define who can connect, to which computers, for what purpose, with which mode, and whether the user must approve access. Document unattended access separately because it creates a different risk. Establish rules for file transfer, commands, stored credentials, session records, customer support, and privileged systems.
Technicians should verify the target before connection and avoid accessing unrelated information. Remote support records can help document service, but retention must be proportionate. Remove access promptly when employment, responsibility, device ownership, or customer assignment changes.
Review server, database, network, endpoint communication, Android and Windows coverage, customer structure, capacity, availability, and recovery.
Evaluate authentication, encryption, roles, firewall policy, credentials, endpoint permissions, logs, patching, backups, and incident response.
Test Remote Desktop, file transfer, commands, support reporting, device grouping, inventory, setup packages, and technician workflows.
Plan pilots, training, upgrades, database maintenance, retention, access reviews, decommissioning, support, and disaster-recovery exercises.
A pilot should reproduce real connection paths and user roles. Measure connection success, response, support resolution, administrative effort, database behavior, report usefulness, and exception handling. Expand only after responsibilities and recovery procedures are understood.
Discuss your infrastructure, Windows and Android endpoints, customer structure, technician permissions, security controls, and support reporting with DeskGate.
Document every component and trust boundary: administration server, SQL database, endpoint service, technician workstation, Android device, network segment, firewall, certificate, backup system, report export, and identity source. Record the owner, update process, monitoring signal, recovery dependency, and permitted communication path for each component.
Capacity planning should include normal and peak connections, screen resolution, endpoint count, database retention, reporting schedules, customer growth, backup duration, and recovery targets. Monitor trends rather than waiting for a capacity incident. Test service restart, database restoration, certificate renewal, network interruption, and administrator loss before the platform becomes business critical.
A cloud service can reduce infrastructure work, while self-hosting can provide stronger control over placement, integration, retention, and administrative boundaries. Neither model is automatically correct for every organization. Compare security capability, available staff, regulatory requirements, customer contracts, uptime objectives, recovery resources, update responsibility, and long-term cost.
DeskGate is designed for organizations that deliberately choose self-hosted administration. The decision should be supported by a named service owner, operating procedures, security review, maintenance calendar, backup evidence, and an escalation route. When these foundations are present, Remote Desktop becomes part of a governed internal platform rather than an isolated connection utility.
Document service-level objectives for connection availability, support response, recovery time, recovery point, and planned maintenance. Monitor the infrastructure components that contribute to those objectives and define escalation when a threshold is missed. Include certificate expiration, database capacity, backup completion, endpoint service health, and administrator access in routine checks. Regular restoration exercises provide stronger evidence than backup status alone.
Review documented architecture annually and after material infrastructure, staffing, customer, security, or regulatory changes. Keep operational contacts and recovery instructions current.